Firewalls are the backbone of all networks and they have come a long way from traditional packet-based filtering firewalls to Next generation firewalls having convention firewall with network device filtering functions involving deep packet inspection, intrusion prevention system (IPS), TLS based encryption, website filtering, QoS / bandwidth management, malware inspection etc.
Today we look more in detail about next generation firewalls such as Juniper SRX firewall and Fortinet firewalls, how they are different from each other, and their features.
Juniper SRX Firewall
Juniper SRX is a single appliance having NGFW functionality, unified threat management (UTM) capability, and secure switching and routing. The SRX firewalls provide network wide threat visibility.
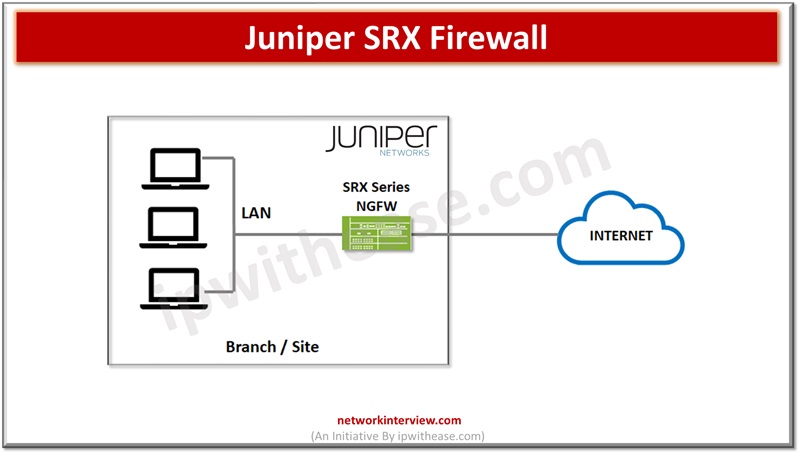
- It provides NGFW capabilities such as full packet inspection, appliance aware, UTM.
- It has inbuilt intrusion prevention to understand application behaviour and weaknesses.
- It defends the network from viruses, phishing attacks, malware, and intrusion.
- Adaptive threat intelligence is performed using spotlight secure to consolidate threat feeds from various sources to provide actionable insights into SRX gateway.
- Role of router and firewall into one appliance with switching capabilities.
- Juniper uses Junos Services Redundancy Protocol (JSRP) to enable it to set up two SRX gateways for high availability.
Fortinet Firewall
Fortinet NGFW works at high speed and inspects encrypted traffic, identifies, isolates, and defuses live threats and protection from threats. Fortinet also provides web filtering, sandboxing, anti-virus, and intrusion prevention system (IPS) capabilities. Performing high speed secure socket layer (SSL) or transport layer (TLS) inspection. Consistent enforcement policies using central policy and device management having zero touch deployments.
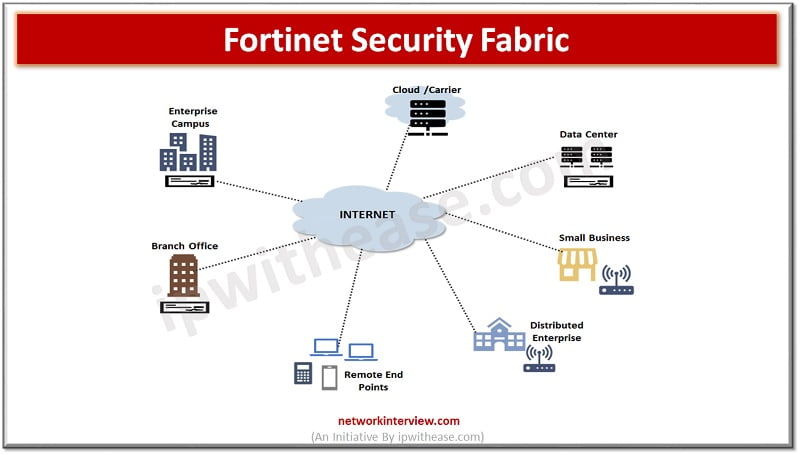
What is common between Juniper SRX firewall and Fortinet Firewall?
- Secure routing where inspection happens to analyze if traffic is legitimate before being forwarded across network
Comparison: Juniper SRX firewall vs Fortinet Firewall
Function | Juniper SRX Firewall | Fortinet Firewall |
| Architecture | Employs a modular architecture using Junos operating system used across devices for consistent and scalable platform | Uses proprietary operating system known as FortiOS. It integrates a range of security features into a single platform |
| Security Features | Advanced threat protection (ATP), intrusion prevention system (IPS), VPN, and unified threat management (UTM) capabilities. | Consolidation of various security capabilities into a single device primarily unified threat management (UTM). In addition of features related to antivirus, antispam, web filtering and application control |
| Proactive security measures such as threat intelligence and analytics | ||
| Performance | High performance hardware and meant for demanding enterprise environments. Scalable to handle network traffic load and security demands | High performance firewalls in terms of throughput and latency. Focus on consolidating security functions to optimize performance and ease of management |
| User Interface | User interface available with Junos space platform for its simplicity and ease of use. Intuitive interface for administrators | User friendly interface and FortiManager central management system to have centralized control of devices. Visualizations and dashboards for network monitoring and security events |
| Scalability | Emphasis on scalability and ideal for both small and large enterprises. Modular architecture to support additional functionality to be added as network grows | Designed with scalability in mind having appliances to cater all network sizes. Consolidation of multiple security functions into a single device offering scalability. |
| Configuration Mode | SRX supports configuration commit method to deploy changes. Let deploy and stage changes and commit changes later as desired. | Fortinet uses configuration tree and post exit the config branch of the tree changes get committed. |
| Commit Rollback Feature | Commit rollback to a pre-existing state is supported | Do not support commit rollback feature |
| IPv6 Support | Better support for IPv6 and routing-based feature DVMRP. | IPv6 is supported with other features like DHCPv6 |
| SSL VPN Support | Juniper requires to buy another appliance for SSL VPN terminations | Supports SSLVPN on appliance |
| Integral Wireless – Controller | Juniper SRX supports wireless Lan controls on large branch model or on bigger appliances with limited AP count | FGT models all support some type of integral WLC and limited support of APs and wireless tunnelling |
| Shell Access | Supports Unix Shell | Do not support Unix shell |
| Security Policies | SRX uses concept of zones and policies are built from one zone to another | Fortinet uses port-based policies and built from one port to another port |
Download: Juniper SRX firewall vs Fortinet Firewall Comparison table
Continue Reading:
Palo Alto vs Fortinet Firewall: Detailed Comparison
Juniper SRX Firewall vs Palo alto Firewall